Customer identity, API keys, audit — the parts your customers see.
Modern SaaS sells to other SaaS, which means your customers' security teams have an opinion. Tessarac ships the customer identity layer (CIAM, B2B multi-tenant, branded UI), the API-key plane your customers' developers will configure, and the per-tenant audit log they'll ask to export — all under one bill.
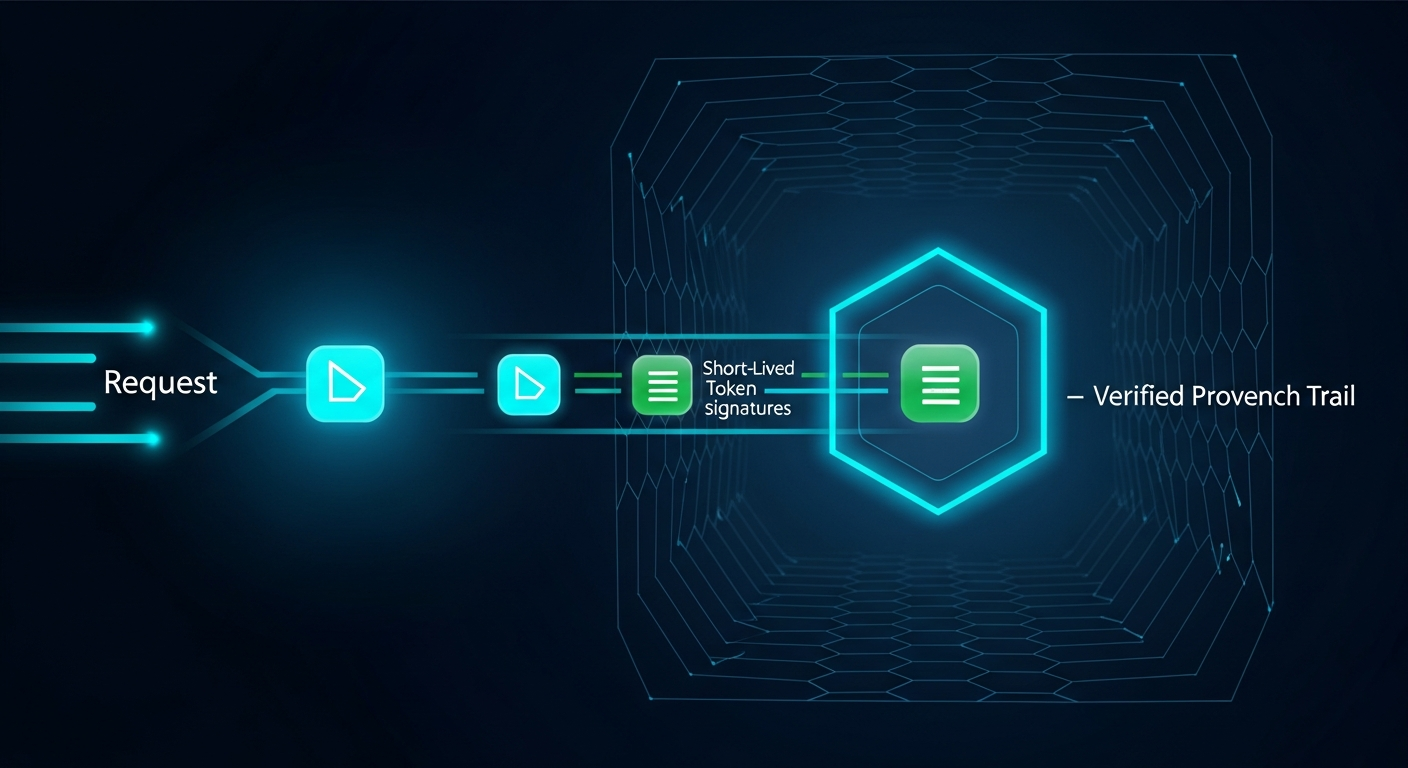
The SaaS-shaped opportunity
The parts your customers ask for, shipped as features instead of build-outs.
Every B2B SaaS hits the same checklist eventually: SSO with the customer's IdP, SCIM provisioning, audit log export, per-customer API keys, branded hosted UI. Most teams build all of that themselves over 18-24 months. Tessarac ships them as configuration, not engineering effort.
- Customer-side SSO into the customer's IdP (Okta, Entra, Google Workspace, JumpCloud) — SCIM 2.0 provisioning
- Branded hosted UI per customer brand — no custom theming engineering
- Per-customer API keys with scopes, rate limits, IP allowlists, hot rotation — the API-key plane your customers will ask for
- Per-tenant audit log surfaced inside the customer's view of your product
- Audit export to the customer's destination — any object-storage bucket, syslog endpoint, or Linux host
The SaaS deployment
One platform for the consumer side (CIAM) and the operations side (workforce). Per-tenant compliance preset surfaces what each customer is audited against.
B2C consumer sign-in
Passkeys, magic links, social federation with 25+ providers. Friction-free path on phones, hardware-key path on workstations. Branded hosted UI per affiliate brand.
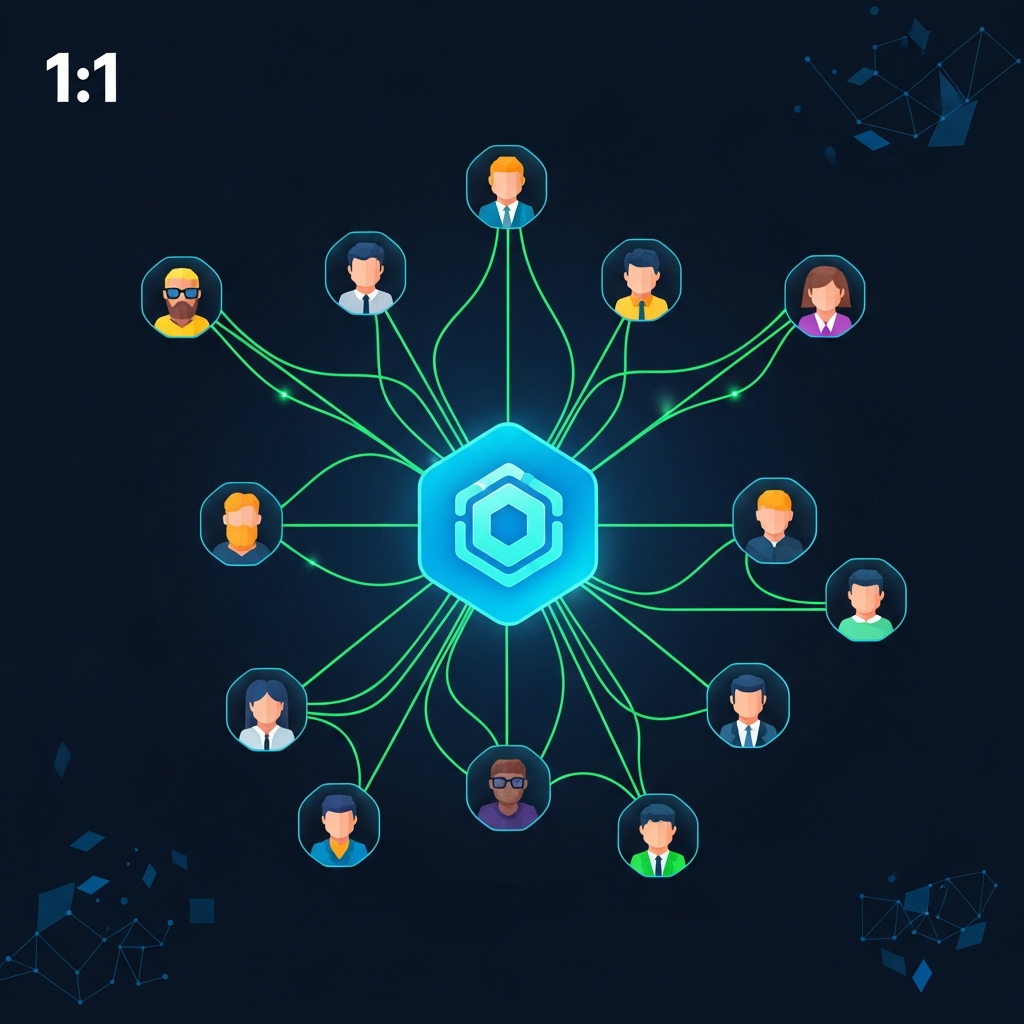
B2B multi-tenant
Org switching, per-org SSO config, per-org branding. Customers connect their own Okta / Entra / Google Workspace as the SSO source. SCIM 2.0 provisioning keeps users in lockstep.
API key plane (customer-facing)
Per-customer keys with scopes, rate limits, IP allowlists, hot rotation. Customers self-service from your branded UI. Per-key usage analytics — your customers see their own; you see the aggregate.
Customer-visible audit
Every login, MFA challenge, policy change, API-key use is captured per tenant. Customers see their own audit log inside their view of your product. Export to any object-storage bucket they own or to a syslog target — opt out of Tessarac retention entirely.
Cost story
Most SaaS teams pay for themselves before the second product is added.
The typical SaaS stack swap is Auth0 (CIAM) + a homemade API-key engineering project + the audit-log SaaS du jour. Tessarac absorbs all three at a single line on your prepaid credit balance. The migration is sized in weeks; the bill comes off in the first month.
- One per-unit price per service across the whole platform — buy prepaid credits as you need them, no per-seat math, no plan tier upcharges
- Includes the first 25,000 monthly active app users free; volume pricing thereafter
- Open-core licensing — pilot the platform on the Community edition before any commercial conversation
- Reference deployments for SaaS on every major cloud (active-active across two regions, multi-regional load balancer, managed-database HA)
Talk to a Tessarac SaaS architect
Most SaaS replacement engagements are sized at 4-8 weeks. CIAM cutover is one allowed-issuer change.